Security for your most valuable AI assets

Nscale protects your models, datasets, and workloads with independent security controls at every layer, from the data center to operations. Every deployment comes with clear responsibilities, so you know which controls we run and which stay with you.
Security designed for AI at scale

AI workloads run across thousands of GPUs for days or weeks, with model weights and datasets spread across many hosts. A breach could expose your data and wipe out weeks of training, so Nscale builds independent security controls into every layer.
Defence in depth

Independent layers of protection are designed so no single control failure exposes your workloads.
Security by default

Encryption, tenant isolation and least-privilege access are built in, not added on.
Independent assurance

ISO/IEC 27001 certification and SOC 2 Type 2 reporting give you third-party evidence for your own compliance reviews.

Eyebrow text

Protection at
every layer

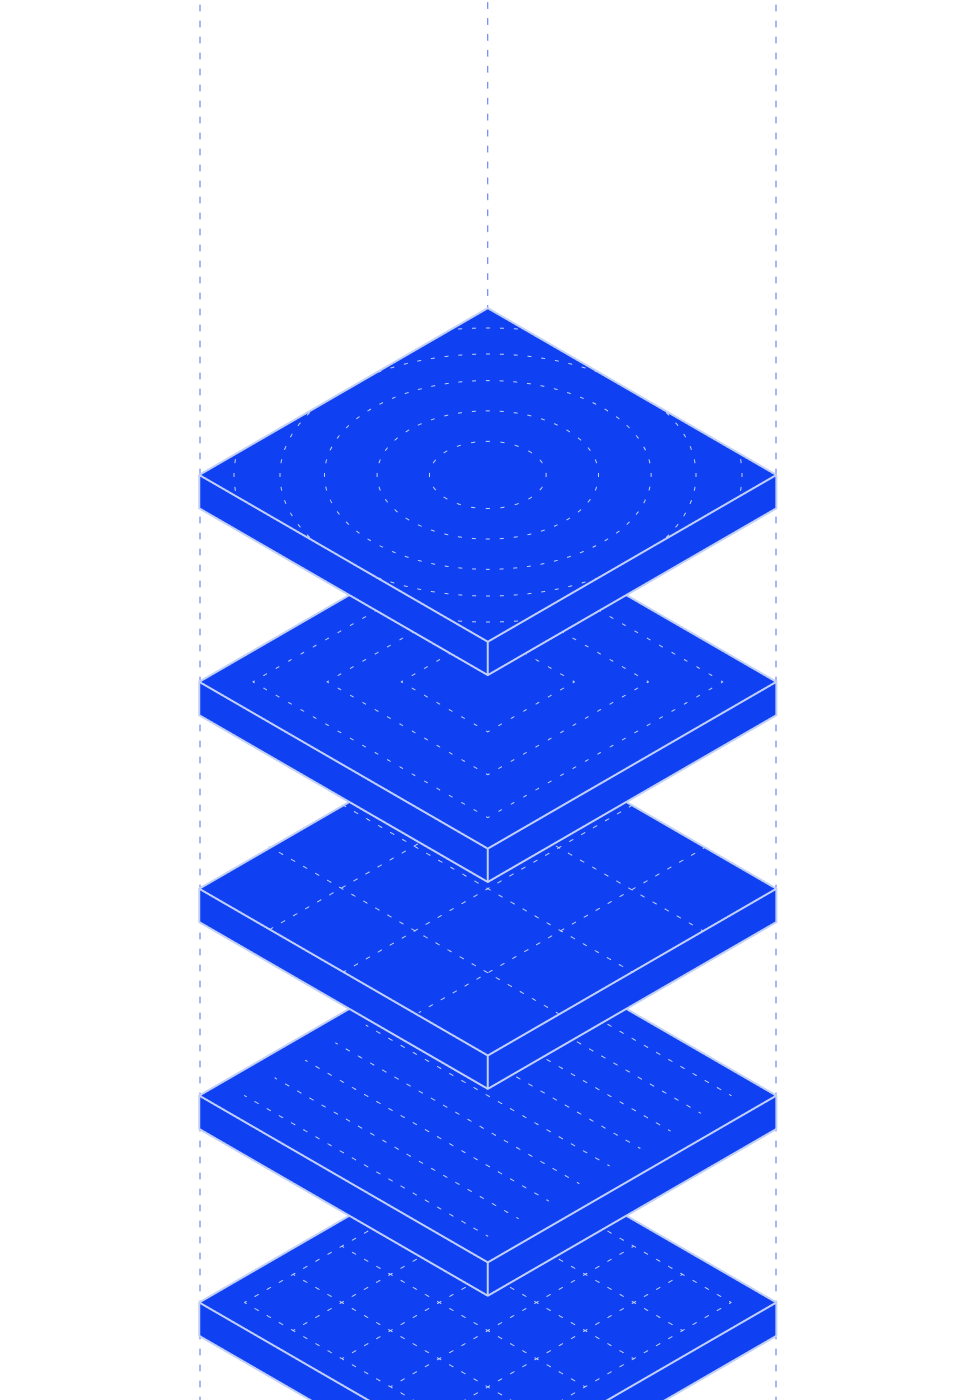
Nscale brings together independent controls across five layers, from the data center floor to day-to-day operations, with each layer strengthening the one above it.
Physical protection starts with controlled access to the hardware running your workloads. Our layered approach includes perimeter security, identity verification, visitor management, monitoring, and 24/7 security operations. Physical access is logged, monitored, and authorized according to business need and least privilege. At colocation facilities, responsibilities between Nscale and the provider are clearly defined.

Customer environments are isolated from one another, and from the privileged management systems used to operate Nscale services. High-bandwidth GPU networking is secured as part of the customer environment. Automated provisioning uses known-good firmware and operating system images, so every system starts from a verified state.

Identity and access management underpins access to customer resources through authentication, least-privilege authorization and audit logging. Nscale Kubernetes Service (NKS) builds on infrastructure tenant separation to support sensitive workloads. Customer platform identity remains separate from the systems Nscale uses to manage its own workforce.

Data stored in Nscale platform services is encrypted at rest and in transit. Key management and data-location controls support customers’ security and sovereignty requirements. Our privacy approach includes collecting personal data for defined purposes, retaining it according to contractual, legal and business requirements, and disposing of it securely when those requirements no longer apply.

Production access is governed through approval and audit mechanisms, with least-privilege permissions and time-limited access for defined tasks. Vulnerabilities are prioritized by risk and remediated against defined service levels.

Monitored and tested around the clock

01

24/7 monitoring and response

Nscale monitors the infrastructure it operates, connecting signals across networks, endpoints, GPU workloads, and identities to detect, investigate and respond to incidents.

02

Continually testing our defenses

Red-team exercises and independent assessments test how our defenses hold up against realistic attack paths. Every finding is owned, prioritized, and retested, and lessons from testing and incidents feed back into our controls.

03

Human-led, AI-assisted security

AI-assisted workflows help our security teams monitor, investigate, and analyze threats at the scale of large GPU fleets. Engineers stay accountable for every outcome, and high-risk actions always require explicit human approval.

FAQs

Nscale’s assurance documents apply to defined services, sites and organizational boundaries. ISO/IEC 27001:2022 covers the information security management system activities and locations listed in the certificate. The SOC 2 Type 2 report covers the Security, Availability and Confidentiality controls of Nscale’s Serverless Inference System, including its supporting data center and operations. Review each document’s scope and reporting period for the exact coverage.

Contact your Nscale account team. They can connect you with our security specialists and provide the certificates, audit reports, testing summaries, and deployment-specific materials available through our customer assurance process. Some documents may require an appropriate confidentiality agreement.

The available storage and processing locations depend on the service and deployment model you select. Nscale agrees the applicable location with you and uses infrastructure controls to enforce it, including where data sovereignty requirements apply. Your account team can confirm the available locations and operating boundaries for your deployment.

Responsibility depends on the service and deployment model. Nscale defines which party is responsible for the infrastructure, identities, workloads, encryption keys, and backups. The responsibility matrix for your deployment sets out the boundary clearly, so your team knows which controls Nscale operates and which controls remain with you.

Nscale’s security, engineering and operations teams work together to investigate, contain and recover from an incident. If it affects your environment, Nscale will communicate promptly through the appropriate channels and keep you informed until the incident is closed. Every incident is reviewed, and the lessons are used to strengthen our controls.

Yes. The Nscale team can connect you with security specialists who can explain the controls, operating responsibilities, and assurance materials relevant to your environment. They can also discuss your architecture, security requirements and the responsibility model for your proposed deployment.

If you believe you have found a security vulnerability in an Nscale product or service, please submit it through our [HackerOne bug bounty program]. Review the program scope and guidelines before testing or submitting a report. Eligible reports may qualify for a bounty.